MassLogger
- 66
- Global rank
- 65
- Month rank
- 86
- Week rank
MassLogger is a credential stealer and keylogger first identified in April 2020. It has been actively used in cyber campaigns to exfiltrate sensitive information from compromised systems. It is designed for easy use by less tech-savvy actors and is prominent for the capability of spreading via USB drives. It targets both individuals and organizations in various industries, mostly in Europe and the USA.
- Keylogger
- Type
- Unknown
- Origin
- 4 January, 2020
- First seen
- 16 October, 2026
- Last seen
How to analyze MassLogger with ANY.RUN
IOCs
IP addresses
- 107.174.192.179
- 48.209.138.189
- 82.29.67.160
- 142.251.20.132
- 104.26.9.202
- 2.23.246.9
- 142.251.13.154
- 142.251.110.102
- 172.211.123.250
- 23.59.18.102
- 142.251.154.119
- 20.166.131.27
- 2.16.204.135
- 142.251.20.155
- 188.114.97.3
- 23.59.17.18
- 150.171.27.11
- 104.26.13.64
- 192.178.183.139
- 185.111.111.157
Hashes
- 74441313bb1fb62500484443c4937e90d4e335351a4fcd12a9ac48448500e33e
- 2ed27c1421e6928dbe13dbfdb5c59e1045b30341fe7ebe05700006bc5ac572c0
- 4094d158e3b0581ba433a46d0dce62f99d8c0fd1b50bb4d0517ddc0a4a1fde24
- 99653a38c445ae1d4c373ee672339fd47fd098e0d0ada5f0be70e3b2bf711d38
- c158322bd963d2a68ffc878d72213a7394d8c16de72279771ffc924365eec0df
- 59345c006cd9bde5ef532aae1f119758d45030993181c272bb0dd6fc0c5d01e5
- 2ae1142b08d296c25000e451237ea919f981da28f6a723d39540f43f18bac762
- 5639c845d56dedecd2cfdb082b734593b5d618a87f1bd8ec612a8b3f4245566a
- 32ae9531405ef3c59448fe6dbd3be435e726eb17f3ca0d16530a4c6317dea286
- 7c68f28c6995f47dd77596bab28c6b4388ff93840c3becfd37733ddb640cd0cd
- 40cf1af5650b699a947899d2b43a00dcb64cdeaf080651c82a7930910c1c03f4
- ec249b0dab6fda20cc24f0f25a504c55a05b23fb6cbb4938aa7a41df0c8744b6
- 0162159b64eb092f94964faf937f263fb9947b25d40e0d82bd3224d136a140de
- 77eed9211cd8464482f0da3fac4c0f003c2b8a6d76f15445927e66400f102d60
- 6558013f984e594bb57534910ce0b17bfa15da3cc9bb4b6e0b5c6e4ddf9eb14e
- a7109b8374dffa7a0cd69558990f7e96fea9ef61736d89043dad5a6694cdfa4a
- 758a0b404b3daadbd0d4e88a0bedf5c21d5507392f7b54d4906ffea49d58ab32
- 558bbe6193a202dcb00cc441421f5d838764e495b8e4d2e10877db7f661b8cd5
- db3ac1fd3d65df45d805adb8dfe0c5209db07ef93406db17dfb783dd8048720a
- 19acfa0adce363a9c9a3be73f5ec0fac0dcf3c630ce18125fd265040ad6ffb6c
Domains
- fundingchoicesmessages.google.com
- pagead2.googlesyndication.com
- copilot.microsoft.com
- t.me
- ip-api.com
- jackthyfuc.run
- laminaflbx.shop
- identitytoolkit.googleapis.com
- fonts.googleapis.com
- plausible.io
- edge.microsoft.com
- tracenep-eu.admaster.cc
- ep1.adtrafficquality.google
- update.googleapis.com
- www.bing.com
- must-directed.gl.at.ply.gg
- uploadnow.io
- oneocsp.microsoft.com
- www.googletagmanager.com
- edge-consumer-static.azureedge.net
URLs
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:qyiwdga5l7ws_4bzfjxxyioxf9ookxt0g7n-czu98sk&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- https://copilot.microsoft.com/c/api/user/eligibility
- https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
- https://uploadnow.io/en/share?utm_source=0bcds7g
- https://cdn.uploadnow.io/_next/static/css/5117ad1bbac15a06.css
- https://cdn.uploadnow.io/_next/static/css/bdb3e22b41fb00da.css
- https://cdn.uploadnow.io/_next/static/css/5ded0d5ca9ecc5c1.css
- https://cdn.uploadnow.io/_next/static/css/56b52b0051b23322.css
- https://cdn.uploadnow.io/_next/static/chunks/framework-76034876ab87df27.js
- https://cdn.uploadnow.io/_next/static/chunks/webpack-601ccb16b36d1888.js
- https://cdn.uploadnow.io/_next/static/chunks/main-8d1cee1b5c7f376f.js
- https://cdn.uploadnow.io/_next/static/chunks/pages/_app-090ad369d35c5500.js
- https://cdn.uploadnow.io/_next/static/chunks/62867-3e700a701aca7086.js
- https://cdn.uploadnow.io/_next/static/chunks/38993-242fdc22cc1c9823.js
Last seen at
What is MassLogger malware?
MassLogger is a sophisticated .NET-based malware classified as a credential stealer and keylogger observed from April 2020. It has since evolved with regular updates from its creator, known as NYANxCAT, who is also linked to other malware like LimeRAT and AsyncRAT.
Its high configurability, evasion techniques, and broad targeting capabilities, as well as the price of approximately $100, made it a popular item on dark web forums. It affects both individual users and organizations, with campaigns targeting industries like manufacturing, banking, and logistics across regions such as Europe (Turkey, Latvia, Italy, etc.), the U.S., and beyond.
MassLogger typically infiltrates networks through social engineering tactics, most often via phishing emails. They may target business users and masquerade as legitimate correspondence, such as procurement requests, shipping notices (e.g., referencing companies like Maersk), or other professional communications.
It can also spread via USB drives by injecting itself into files, infecting new systems when those files are opened.
In some campaigns, MassLogger has been distributed via compiled HTML files (.chm), which, when opened, execute embedded JavaScript to initiate the infection chain.
The infection chain is often multi-staged, involving scripting languages like PowerShell and .NET assemblies, making it harder to trace back to the initial vector.
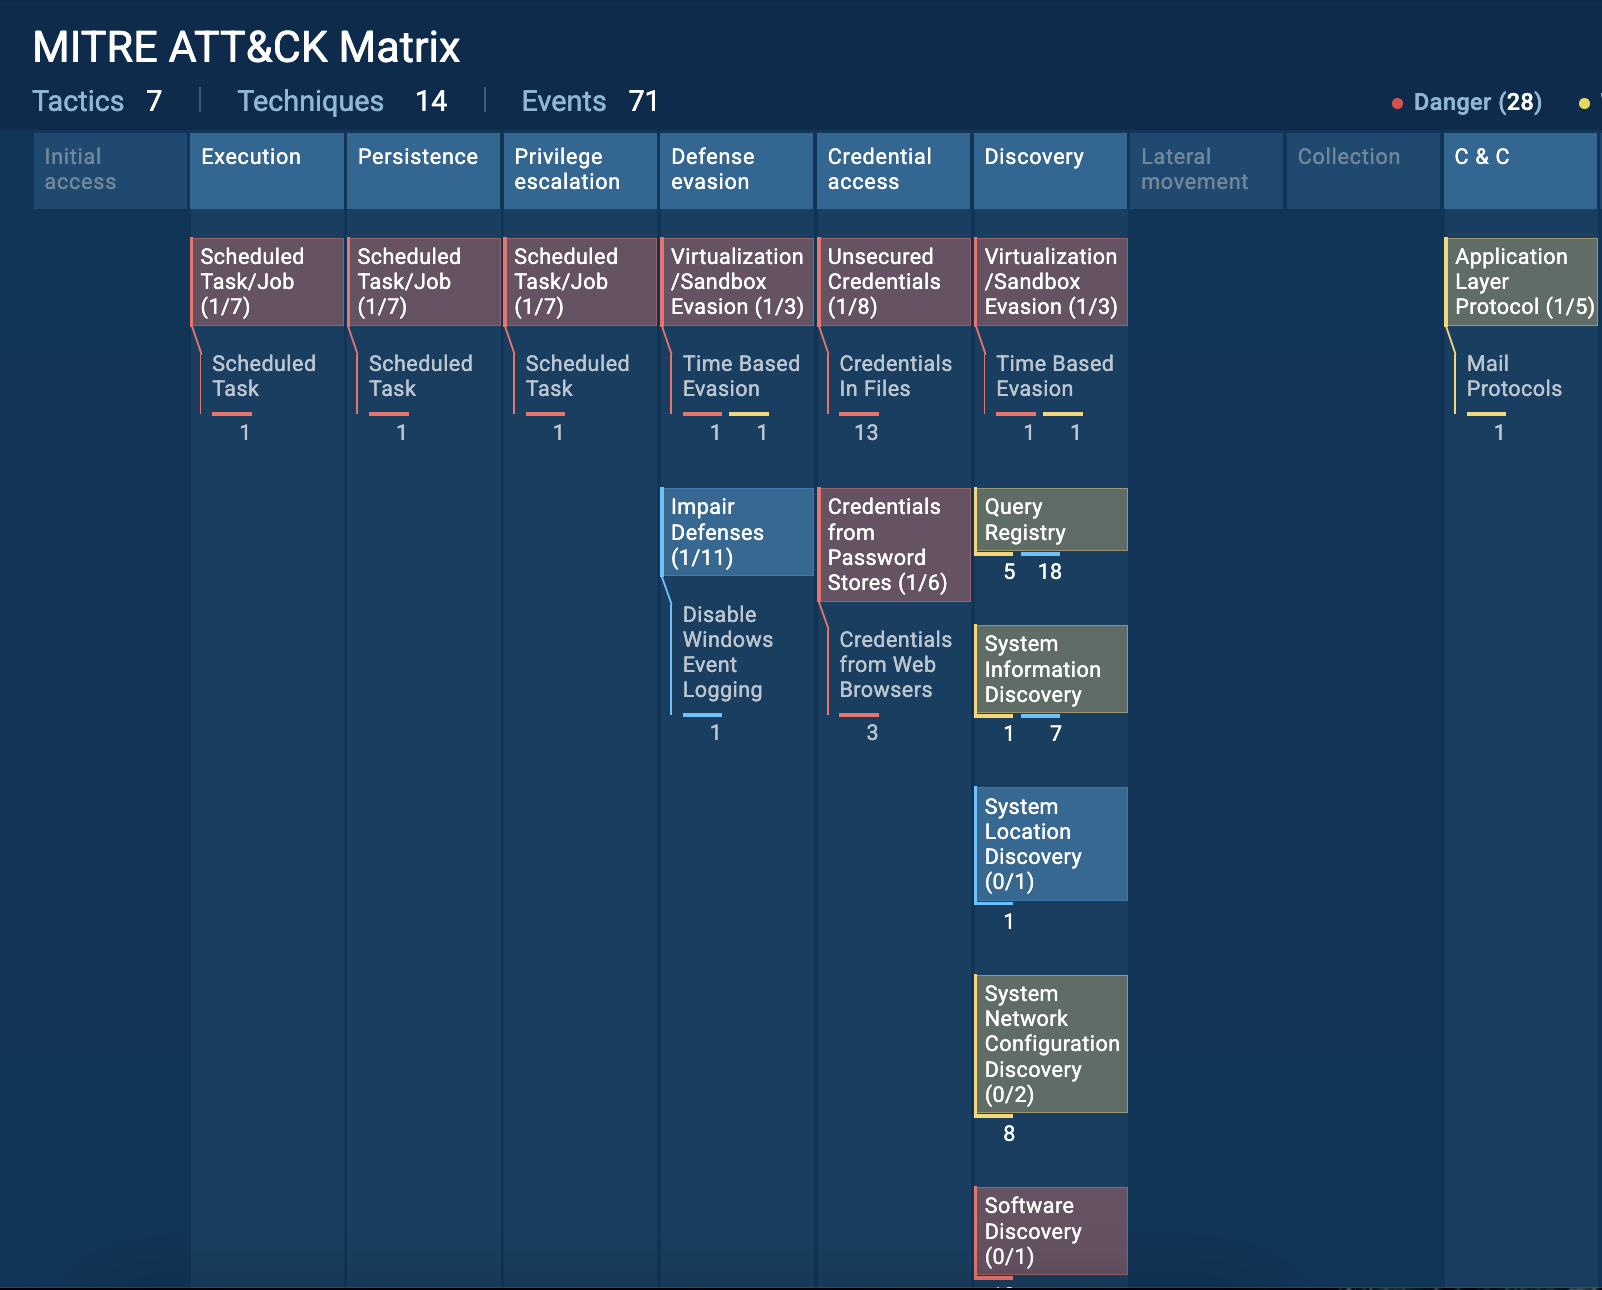
MassLogger is highly efficient at collecting and exfiltrating data. It extracts credentials from a wide range of applications, including web browsers (Chrome, Firefox, Edge), email clients (Outlook, Thunderbird, Foxmail), messaging apps (Discord, Telegram, Pidgin), VPN services (NordVPN), and FTP clients (FileZilla). It can also extract cryptocurrency wallet data.
Besides, it engages keylogging, clipboard monitoring, screen capturing, gathering system info via WMI queries.
MassLogger Stealer’s prominent features
- Abuses USB drives to infiltrate systems via infected files
- To faster achieve its goals and avoid detection, can work without persistence mechanisms
- Extracts data from a wide range of apps, including browsers, messengers, VPNs, network clients etc.
- Available as a Malware-as-a-Service (MaaS) tool for $100 which amplifies its reach
- The focus on fresh session cookies and 2FA bypass (via anti-detect browsers) heightens its threat to modern authentication systems.
MassLogger execution process and technical details
All the variety of MassLogger’s vicious ways is illustrated by fresh malware samples and analyses in ANY.RUN’s Interactive Sandbox. Let’s view one of the recent analysis sessions.
See MassLogger’s sample in action
The intrusion often begins with a phishing email containing a malicious attachment — typically a RAR-compressed archive with an unusual filename extension, such as .chm or .pif — used to bypass email filters. In the past, Microsoft Office files were also commonly used.
The main payload is a variant of the MassLogger Trojan, designed to retrieve and exfiltrate user credentials from various applications, including web browsers, email clients, and VPNs. After the payload is decrypted, MassLogger parses its configuration to target specific applications.
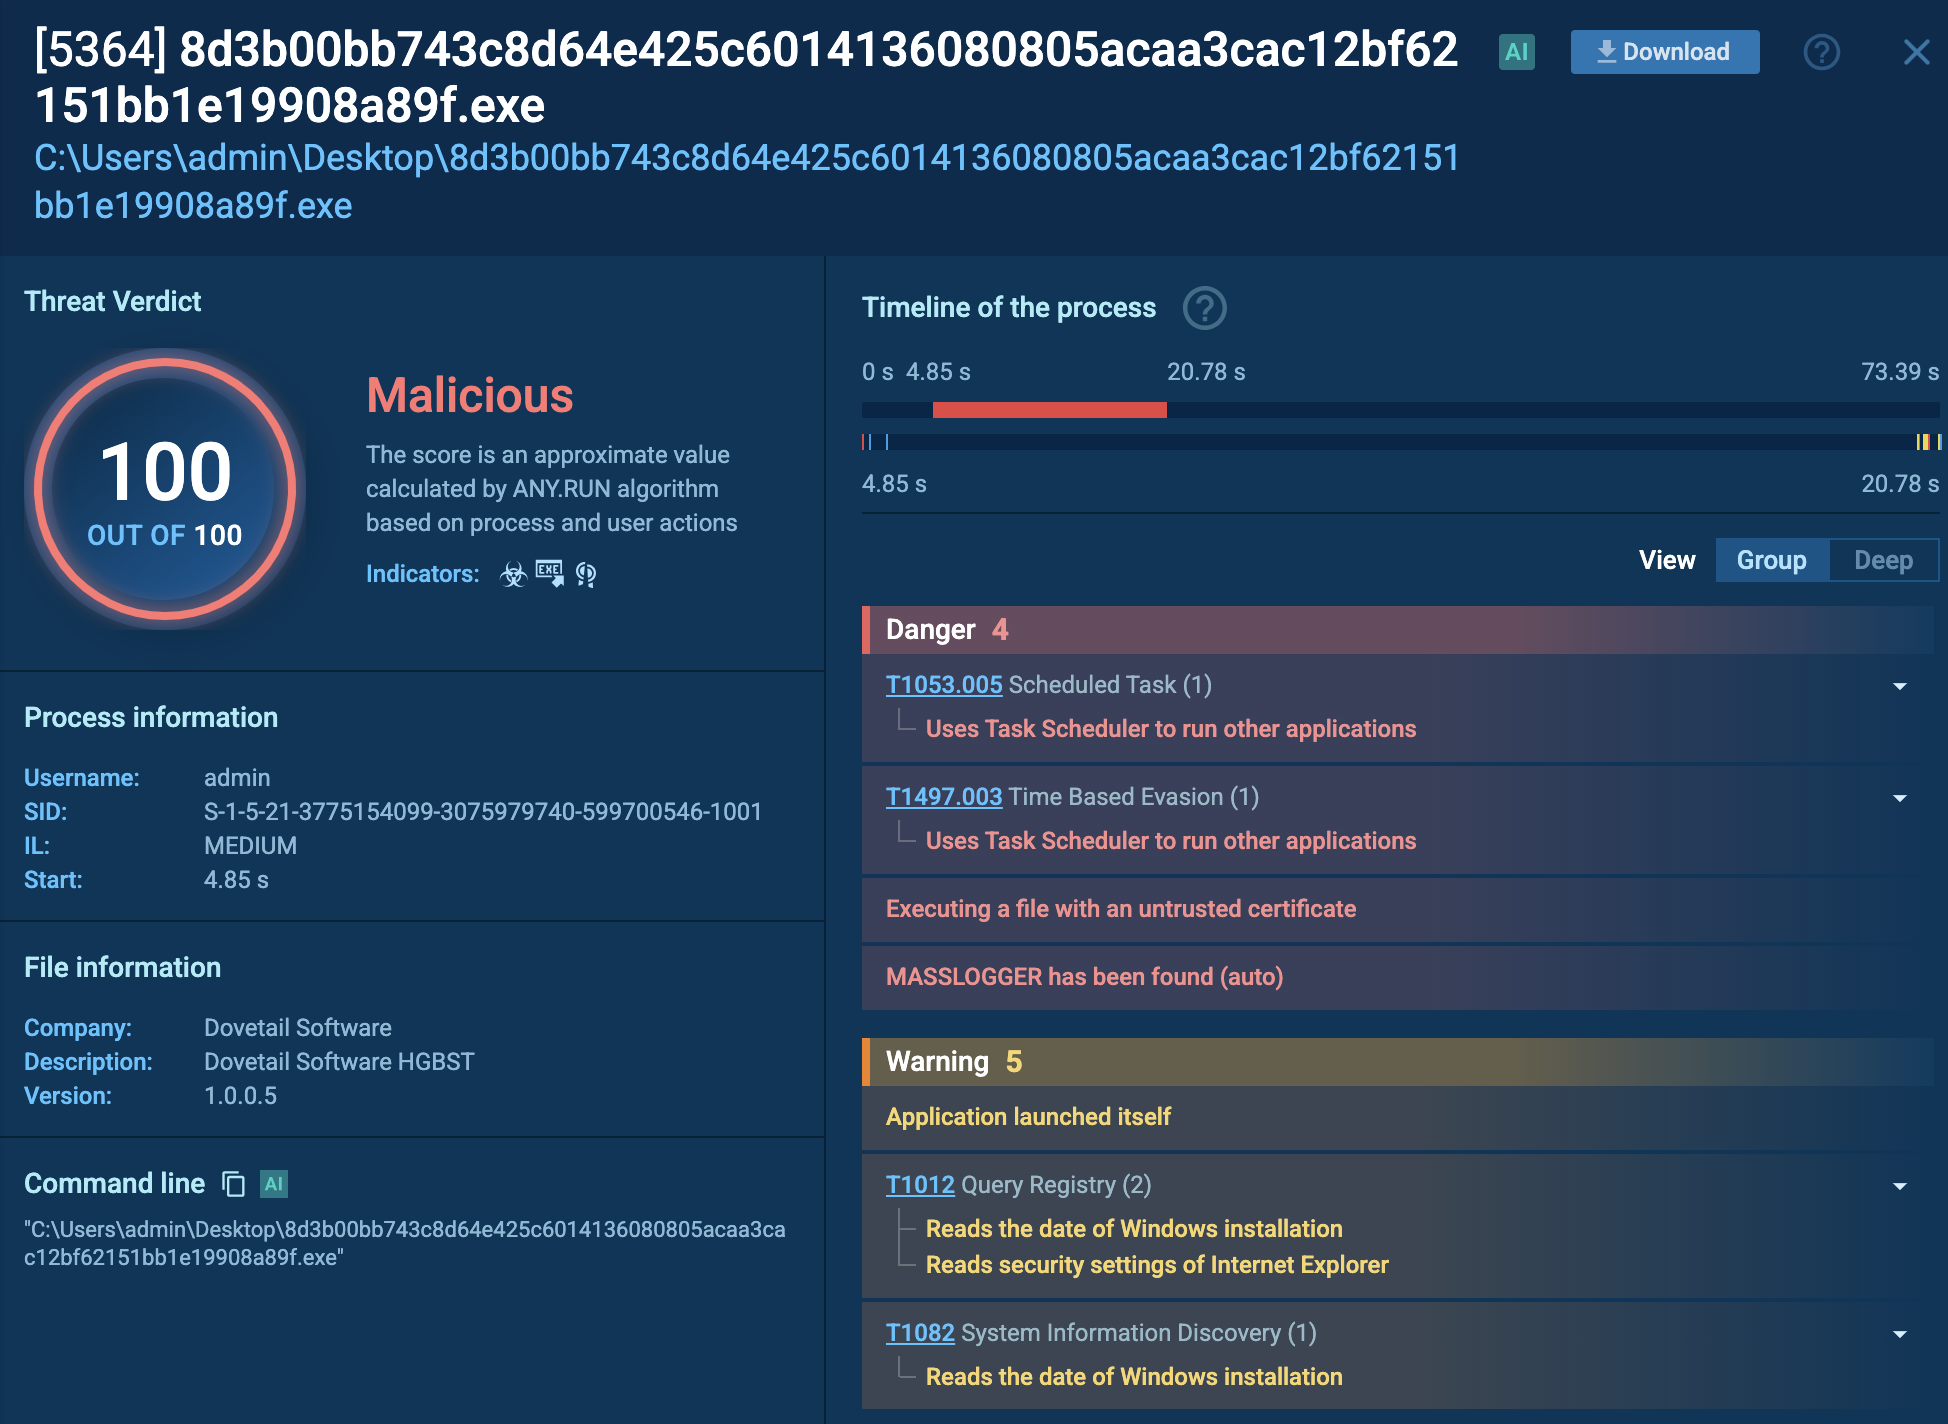
In some cases, it may be configured as a keylogger, though this functionality is often disabled depending on the campaign. The malware collects credentials from targeted applications and stores them in a log file — typically named Log.txt — in a temporary directory within %APPDATA%. Sometimes, it sends stolen information directly from memory without writing it to disk.
The stolen credentials are exfiltrated using methods such as FTP (File Transfer Protocol) or SMTP (Simple Mail Transfer Protocol). In certain scenarios, the data is sent via email to a compromised mailbox, encoded in Base64. MassLogger generally does not persist on the system after execution, meaning it does not install components that would automatically restart upon a system reboot. It also does not request updates from the threat actor over time, making it a relatively straightforward yet effective credential-stealing tool.
MassLogger employs several advanced evasion techniques:
- Obfuscation: Its .NET code is heavily obfuscated, using techniques like polymorphic string encryption, hash-based import resolution, and indirect method calls to hide its control flow from static analysis. Tools like de4dot can partially deobfuscate it, but the latest versions (e.g., v3) use complex interpreters and uninitialized field calls.
- Anti-Analysis: It checks for virtualization or sandbox environments and terminates if detected. It also looks for security software like Avast or AVG, halting execution if found.
- Dynamic Execution: By replacing Microsoft Intermediate Language (MSIL) at runtime, it thwarts static analysis tools like dnSpy, requiring dynamic analysis to reveal its true behavior.
- Fileless Techniques: Operating in memory rather than writing to disk minimizes detectable artifacts.
- Encrypted Configuration: Its configuration (e.g., C2 server details) is encrypted within the payload, decrypted only at runtime using standard .NET cryptographic functions.
- *Legitimate Traffic Mimicry: Exfiltration over SMTP or FTP blends with normal network traffic, avoiding suspicion from basic monitoring tools.
These tactics make MassLogger a "noisy" yet stealthy stealer, balancing aggressive data theft with efforts to remain undetected.
What are the examples of successful MassLogger campaigns?
- Compiled HTML (CHM) Campaign (Early 2021): Cisco Talos documented a significant MassLogger campaign notable for its use of Microsoft Compiled HTML Help (.CHM) files as the initial infection vector. This marked a shift from earlier delivery methods, showcasing the malware’s adaptability. Attackers sent phishing emails with subjects like “Domestic customer inquiry” or “MOU Information,” targeting users in Europe. The emails contained RAR attachments that, when extracted, revealed .CHM files embedding JavaScript to launch the infection chain.
- Procurement-Themed Phishing Wave (August 2021): Cyberint Research identified a series of campaigns in August 2021 targeting manufacturing and banking sectors, particularly in Europe, with phishing emails disguised as procurement requests. Emails included attachments like RAR files or Office documents with macros, delivering MassLogger to steal credentials from browsers, email clients, and VPN services. The malware exfiltrated data via SMTP to compromised mailboxes, storing stolen information in a "Log.txt" file in the %APPDATA% directory.
- XLS-Based Industrial Targeting (March 2025): A recent campaign, noted in posts on X around March 30, 2025, involved phishing emails with fake procurement themes and malicious Excel (.XLS) files distributing MassLogger. It focused on stealing sensitive data from business applications, with exfiltration via SMTP or HTTP to attacker-controlled servers. The global scope and industrial focus suggested a continuation of MassLogger’s evolution into a tool for both broad and targeted attacks, potentially linked to initial access brokers supplying larger cybercrime groups.
These campaigns highlight MassLogger’s key strengths: its configurability, low entry cost, and evasion tactics like obfuscation, fileless execution, and anti-analysis checks. Unlike headline-grabbing ransomware attacks, MassLogger’s impact is often quieter but insidious, focusing on credential theft that can lead to downstream breaches.
Gathering threat intelligence on MassLogger
Threat intelligence is of much help in proactive defending against MassLogger. Use ANY.RUN’s Threat Intelligence Lookup to gather IOCs, study attackers’ TTPs, preempt incidents by blocking known C2 infrastructure.
Start by searching MassLogger in TI Lookup by the name and explore malicious samples that the cybersecurity community using ANY.RUN’s tools have encountered.
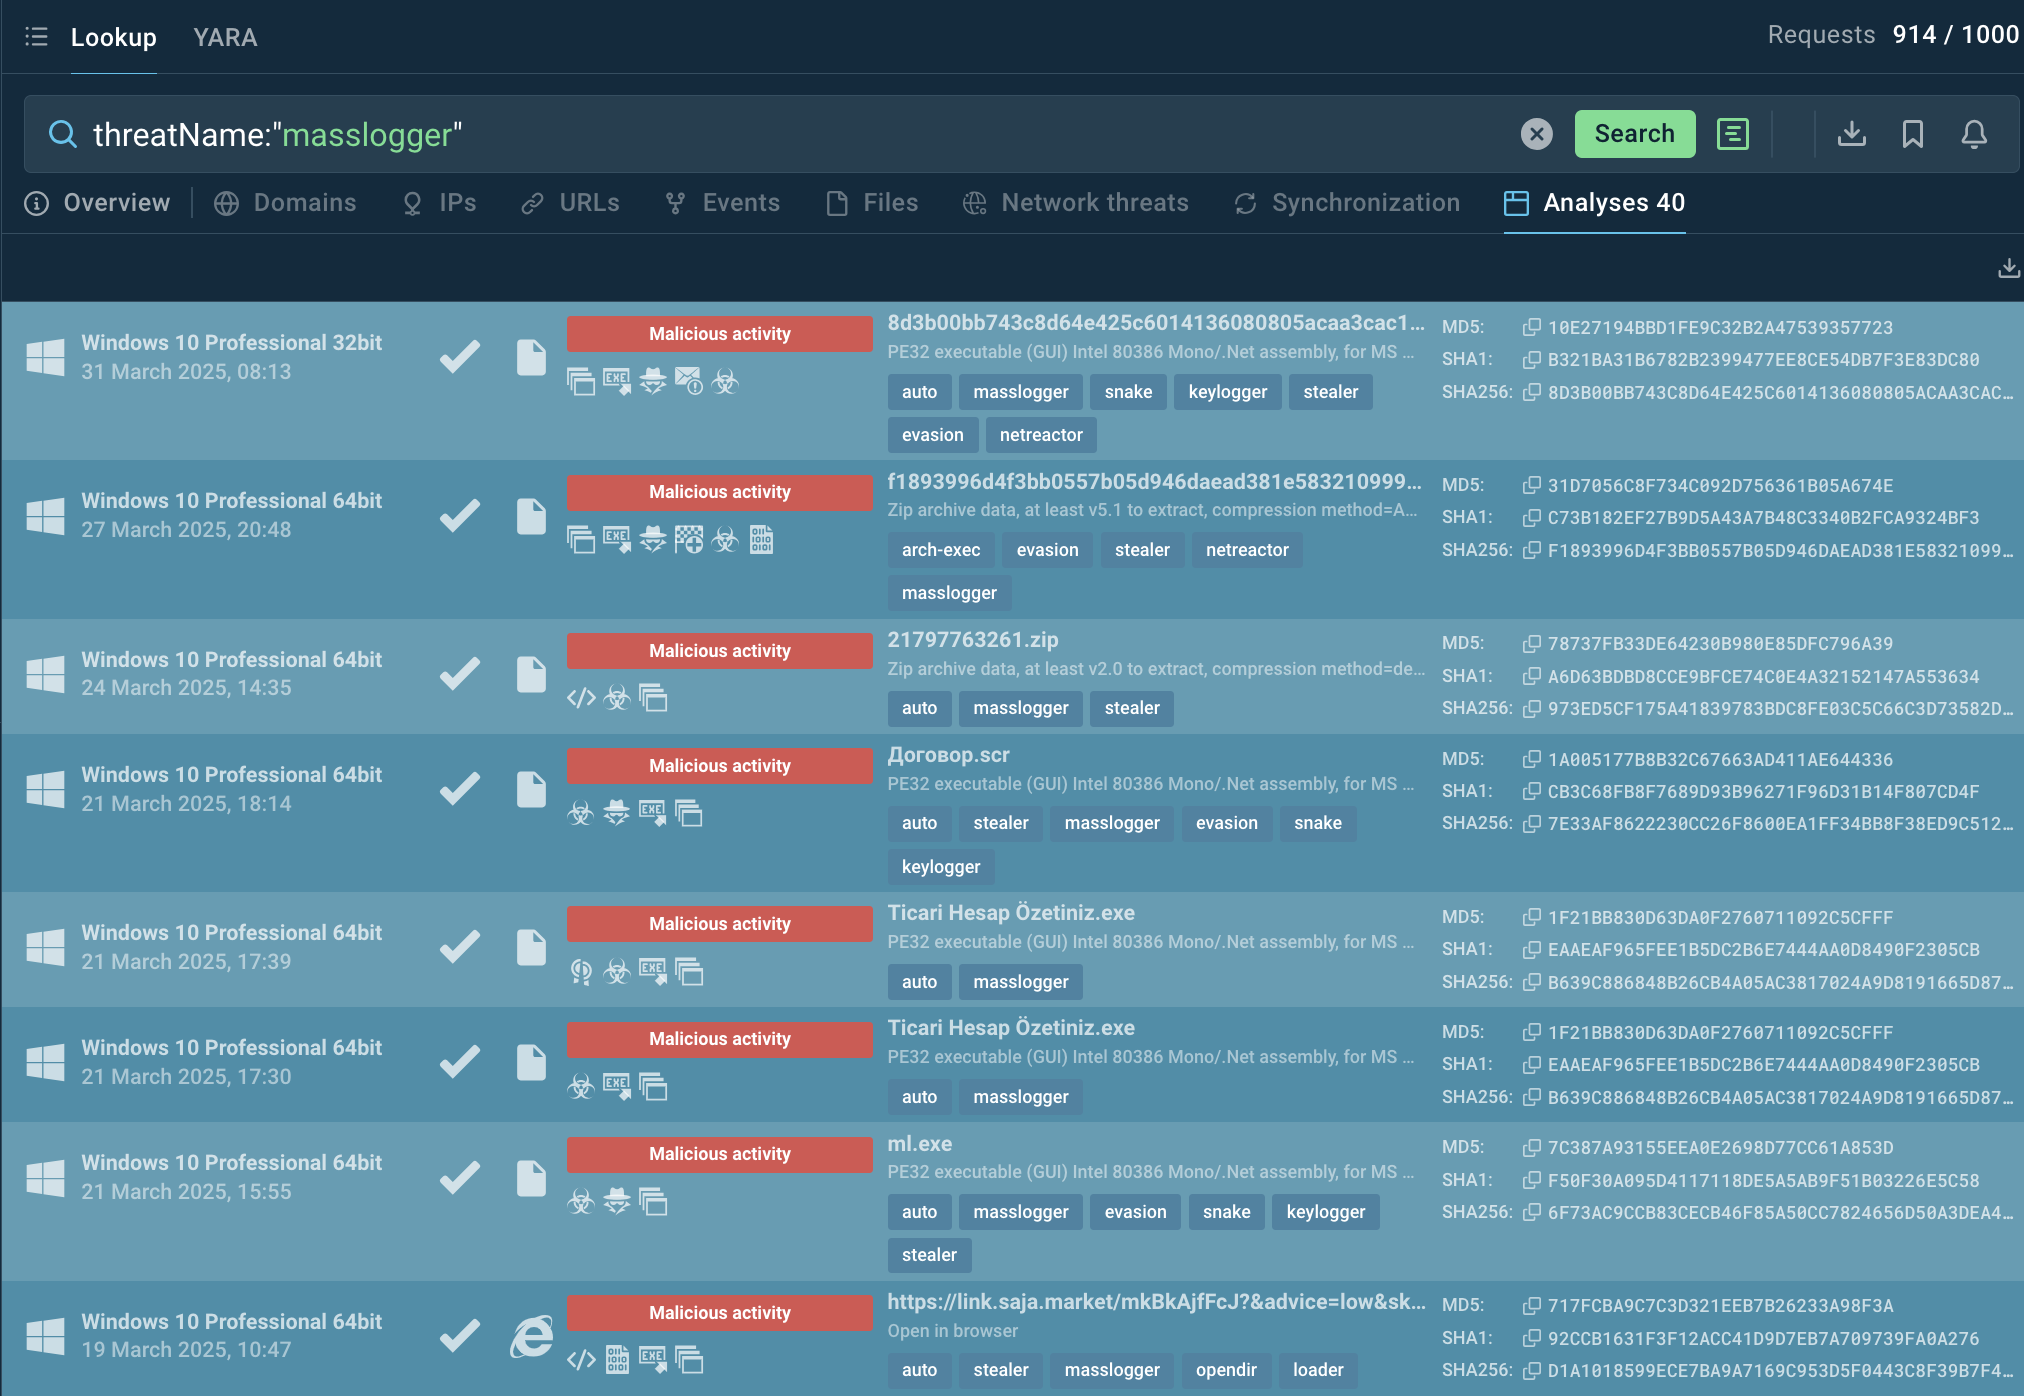
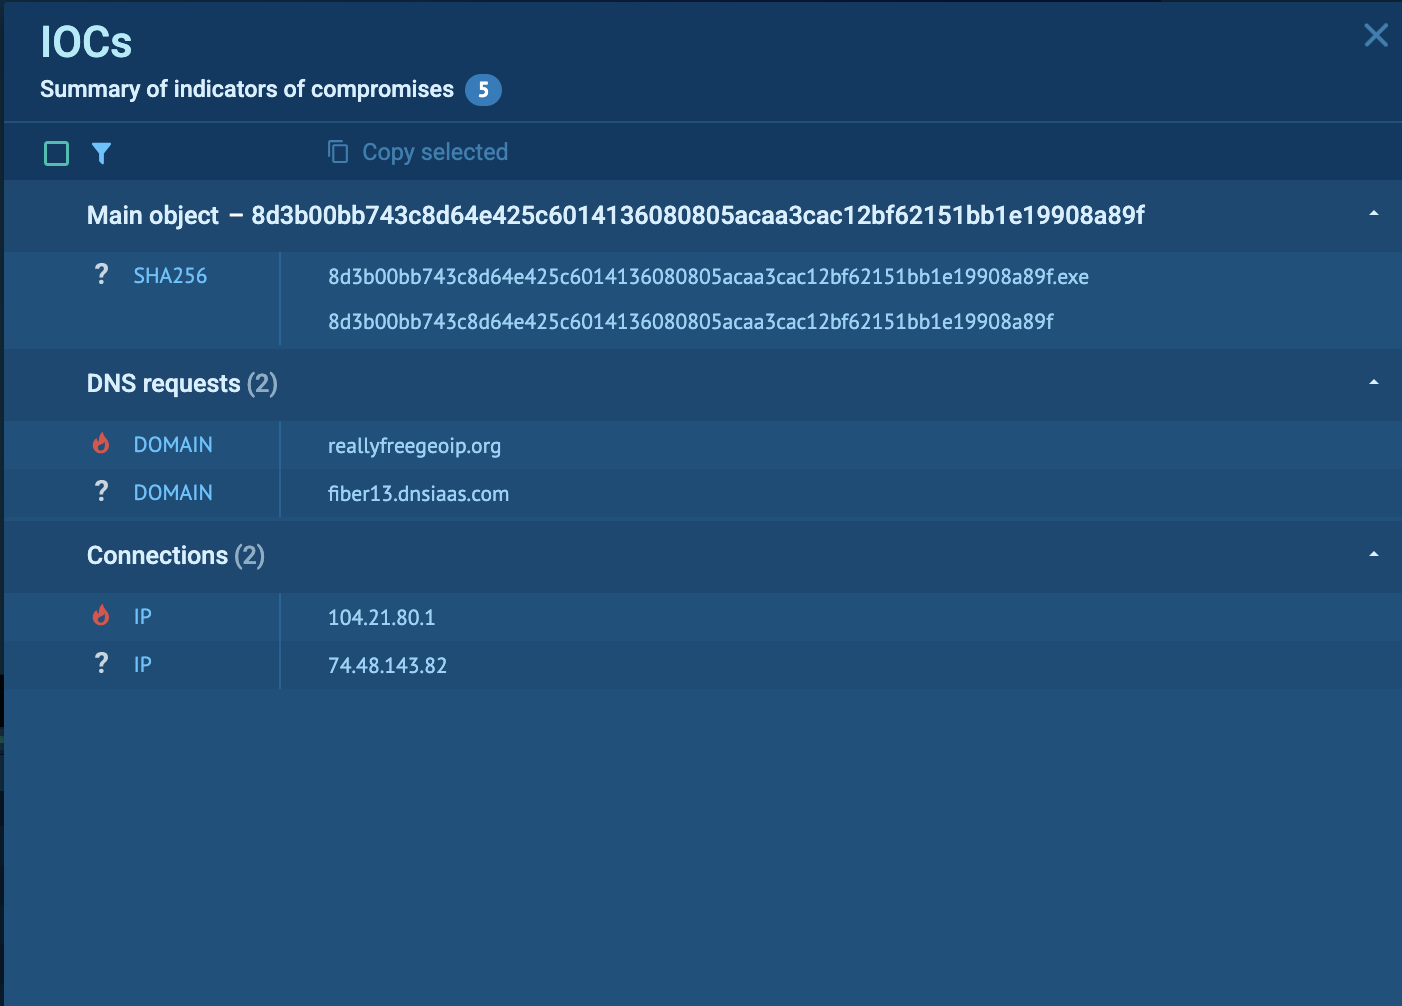
Explore each session to collect new IOCs and use them for further research. Enrich your monitoring and detection systems with the harvested indicators.
Conclusion
MassLogger’s combination of accessibility, evasion tactics, and broad data theft capabilities makes it a formidable threat. Its reliance on phishing and fileless execution demands robust email security and endpoint protection, while its stealth requires advanced threat intelligence to stay ahead of evolving campaigns.
By combining behavioral detection, network monitoring, and proactive intelligence-driven countermeasures, organizations can effectively mitigate its risks.
Start building your defenses against MassLogger with 50 requests in TI Lookup
Other malware & phishing threats
 CephalusCephalus is a targeted ransomware threat discovered in 2025. It’s known for infiltrating organizations that deal with sensitive data through compromised RDP access. It leverages DLL sideloading with a legitimate SentinelOne executable. Cephalus is able to exfiltrate data and destroy backup options. Its payload is also tailored to each victim, which makes identification and mitigation more complex.
 DarkTortillaDarkTortilla is a crypter used by attackers to spread harmful software. It can modify system files to stay hidden and active. DarkTortilla is a multi-stage crypter that relies on several components to operate. It is often distributed through phishing sites that look like real services.
 SmartLoaderSmartLoader is a Windows malware loader that uses multi-stage execution to deliver secondary payloads. It supports system discovery, screenshot capture, persistence through scheduled tasks, C2 communication, and anti-analysis techniques.
 ZloaderZloader is a banking trojan that uses webinjects and VNC clients to still banking credentials. This Trojan is based on leaked code from 2011, but despite its age, Zloader’s popularity has been only increasing through early 2020, when it relied on COVID-19 themed attacks.
 GravityRATGravityRAT is a sophisticated spyware and remote access trojan that has been actively targeting organizations and government entities since 2016. It uses innovative anti-analysis techniques and made an evolution from a Windows-only threat to a cross-platform espionage tool capable of compromising Windows, Android, and macOS systems.
 DarkVisionDarkVision RAT is a low-cost, modular Remote Access Trojan that gives attackers remote control of infected Windows hosts. Initially observed around 2020 and sold in underground marketplaces, DarkVision has become notable for its full feature set (keylogging, screen capture, file theft, remote command execution and plugin support) and for being distributed via multi-stage loaders in recent campaigns.